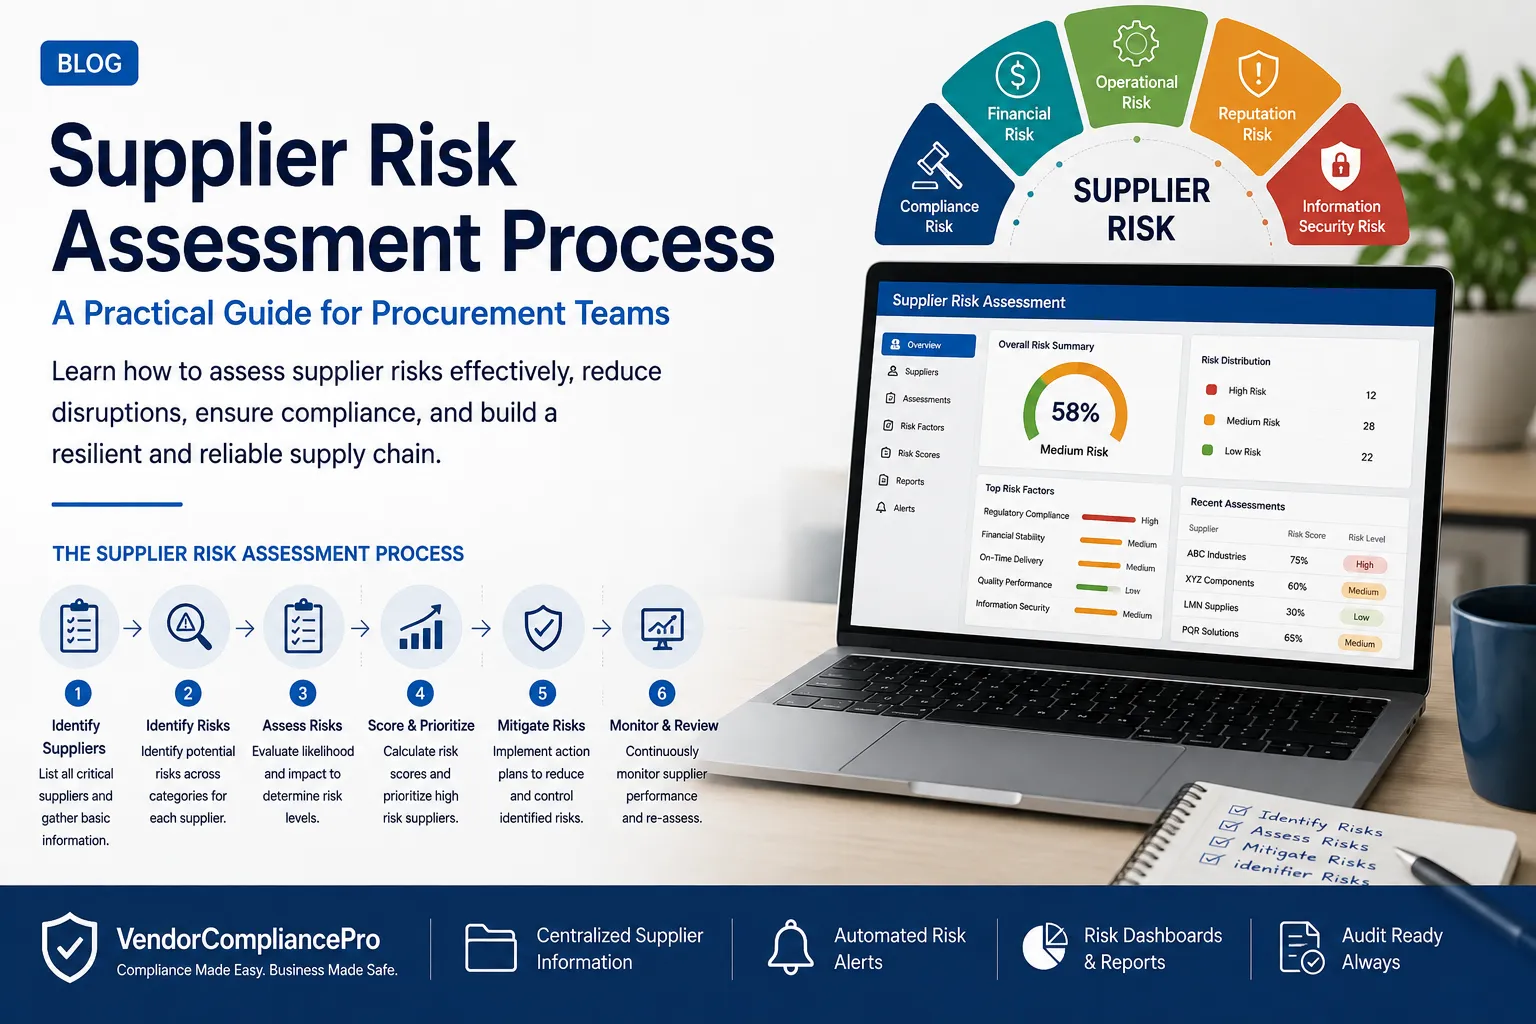
Supplier Risk Assessment Process: A Practical Guide for Procurement Teams
A supplier may look reliable when everything is going well.
But what happens when a critical supplier suddenly stops delivering, quality problems increase, an important compliance document expires, or the supplier experiences financial difficulties?
This is why procurement teams need a structured supplier risk assessment process.
Supplier risk assessment helps organizations identify, evaluate, score, prioritize, mitigate, and monitor risks associated with suppliers.
Instead of treating every supplier in the same way, organizations can assess suppliers based on:
- Supplier criticality
- Financial exposure
- Operational dependency
- Quality performance
- Delivery performance
- Compliance status
- Cybersecurity exposure
- Business impact
In this guide, we will explain a practical supplier risk assessment process that procurement teams can use from supplier onboarding through ongoing supplier monitoring.
What Is Supplier Risk Assessment?
Supplier risk assessment is the process of identifying and evaluating the risks associated with a supplier before and during the supplier relationship.
The objective is not to eliminate every possible risk.
The objective is to understand:
- Which suppliers create the greatest risk?
- What type of risk does each supplier create?
- How serious could the impact be?
- How likely is the risk to occur?
- What controls are already in place?
- What action should be taken?
- When should the supplier be reassessed?
A structured assessment allows procurement teams to prioritize their efforts instead of treating every supplier equally.
Supplier Risk Assessment Process at a Glance
A practical supplier risk assessment process can be organized into six core stages:
| Stage | What Procurement Teams Do | Main Outcome |
|---|---|---|
| 1. Identify suppliers | Build a supplier inventory and assess criticality | Supplier risk population |
| 2. Identify risk factors | Define financial, operational, quality, compliance, and other risks | Risk criteria |
| 3. Assess risks | Evaluate likelihood and business impact | Individual risk assessment |
| 4. Score and prioritize | Calculate risk scores and assign risk levels | Low, medium, high, or critical |
| 5. Mitigate risks | Define controls, corrective actions, and contingency plans | Risk treatment plan |
| 6. Monitor and review | Reassess suppliers and track changes | Ongoing supplier risk visibility |
The process should not end after onboarding. Supplier risk can change as business conditions, supplier performance, contracts, compliance status, and dependencies change.
Why Supplier Risk Assessment Matters
Organizations often depend on suppliers for critical products, services, raw materials, logistics, maintenance, technology, and other business activities.
A supplier problem can therefore become an organizational problem.
Supplier risks can lead to:
- Supply chain disruptions
- Production delays
- Quality problems
- Compliance issues
- Financial losses
- Customer dissatisfaction
- Increased procurement costs
- Data security concerns
- Reputational damage
- Audit findings
- Business continuity problems
The larger and more complex the supplier network becomes, the more important a structured risk assessment process becomes.
A risk-based approach also helps procurement teams focus resources where they matter most.
Supplier Risk Assessment vs Supplier Risk Management
These terms are related but represent different activities.
Supplier Risk Assessment
Supplier risk assessment is the process of identifying and evaluating supplier risks.
It answers questions such as:
- What risks does this supplier create?
- How likely are those risks?
- What would happen if they occurred?
- What is the supplier’s current risk level?
Supplier Risk Management
Supplier risk management is the broader ongoing process of:
- Identifying risks
- Assessing risks
- Prioritizing risks
- Mitigating risks
- Monitoring risks
- Reviewing controls
- Responding to changes
In simple terms:
Risk assessment tells you what the risk is.
Risk management determines what you do about it.
Common Types of Supplier Risk
Supplier risk is not limited to financial problems.
A useful supplier risk assessment should consider multiple categories.
1. Financial Risk
Financial problems can affect a supplier’s ability to continue operations.
Potential indicators include:
- Financial instability
- Significant debt
- Cash-flow problems
- Declining business performance
- Payment difficulties
- Dependence on a small number of customers
- Business continuity concerns
Critical suppliers may require more frequent financial reviews.
2. Operational Risk
Operational risk relates to the supplier’s ability to deliver products or services consistently.
Examples include:
- Capacity limitations
- Production interruptions
- Poor delivery performance
- Lack of backup facilities
- Dependence on a single location
- Inadequate processes
- Weak business continuity planning
Operational risk is particularly important when a supplier provides critical materials or services.
3. Compliance Risk
Suppliers may need to meet legal, regulatory, contractual, or industry-specific requirements.
Compliance risk can involve:
- Expired licenses
- Missing registrations
- Expired insurance
- Missing statutory documents
- Non-compliance with contractual requirements
- Incomplete supplier documentation
Compliance risk can increase over time because documents and certificates may expire.
This is why supplier compliance should be monitored continuously rather than checked only during onboarding.
4. Quality Risk
Supplier quality problems can affect production, customers, and an organization’s reputation.
Indicators may include:
- High rejection rates
- Repeated quality complaints
- Failed inspections
- Product defects
- Inconsistent specifications
- Corrective actions that remain unresolved
Quality performance should be considered when assessing supplier risk.
5. Delivery and Supply Chain Risk
A supplier may be financially stable but still create significant operational risk if deliveries are unreliable.
Consider:
- On-time delivery performance
- Lead times
- Delivery delays
- Capacity
- Geographic dependency
- Transportation risks
- Single-source dependency
- Emergency response capability
- Availability of alternative suppliers
Critical suppliers should have clearly defined delivery expectations and contingency plans.
6. Cybersecurity and Information Security Risk
Suppliers may have access to business systems, confidential information, customer data, or operational information.
Depending on the relationship, organizations may need to assess:
- Security controls
- Access management
- Data protection
- Incident response
- Business continuity
- Security certifications
- Third-party access
The level of assessment should depend on the supplier’s access and the sensitivity of the information involved.
7. Reputation and Business Risk
A supplier’s actions can affect the reputation of the organization they serve.
Potential concerns include:
- Regulatory violations
- Serious customer complaints
- Ethical concerns
- Negative business practices
- Repeated contractual problems
- Significant business disruption
Organizations should consider reputational exposure when assessing strategically important suppliers.
The 6-Step Supplier Risk Assessment Process
Step 1: Identify the Suppliers
The first step is to understand which suppliers are part of the organization’s supply network.
Create a supplier inventory containing information such as:
- Supplier name
- Supplier category
- Products or services
- Business location
- Supplier criticality
- Departments using the supplier
- Contract information
- Compliance requirements
- Alternative supplier availability
Not every supplier will have the same importance.
For example, a supplier providing office stationery may have relatively low business impact.
A supplier providing a critical production component may have a much higher impact.
Supplier criticality should therefore be considered early in the assessment process.
Step 2: Identify Supplier Risk Factors
After identifying suppliers, determine which risk factors are relevant.
A procurement team can create a standard risk assessment questionnaire or checklist.
Typical areas include:
Business Risk
- Supplier criticality
- Dependency on the supplier
- Number of alternative suppliers
- Geographic dependency
- Business continuity
Financial Risk
- Financial stability
- Business performance
- Cash-flow concerns
- Customer concentration
- Business continuity
Operational Risk
- Production capacity
- Delivery performance
- Business continuity planning
- Facility dependency
Quality Risk
- Quality history
- Rejection rates
- Customer complaints
- Corrective actions
Compliance Risk
- Required registrations
- Licenses
- Insurance
- Statutory documents
- Contractual requirements
Security Risk
- Data access
- System access
- Information security controls
- Third-party access
The assessment should be appropriate to the supplier and the nature of the relationship.
A low-risk supplier does not necessarily need the same depth of assessment as a critical supplier with access to sensitive systems.
Step 3: Assess the Risks
Once the risk factors are defined, evaluate each supplier.
A simple approach is to consider two primary dimensions:
Likelihood
How likely is the risk to occur?
Impact
How serious would the business impact be if the risk occurred?
For example:
| Likelihood | Impact | Example Risk Level |
|---|---|---|
| Low | Low | Low |
| Low | High | Medium |
| Medium | Medium | Medium |
| High | Medium | High |
| High | High | Critical |
Organizations can create more detailed scoring models when required.
The scoring model should be consistent so that procurement teams can compare suppliers using the same general framework.
Step 4: Score and Prioritize Suppliers
A risk score helps procurement teams prioritize suppliers.
One simple approach is to use a 1-to-5 scale.
Likelihood
- 1 = Very Low
- 2 = Low
- 3 = Medium
- 4 = High
- 5 = Very High
Impact
- 1 = Very Low
- 2 = Low
- 3 = Medium
- 4 = High
- 5 = Very High
A basic risk score can then be calculated using:
Risk Score = Likelihood × Impact
For example:
Likelihood = 4
Impact = 5
Risk Score = 20
The organization can then define its own thresholds for low, medium, high, or critical risk.
The exact scoring model should be aligned with the organization’s risk framework.
Step 5: Create a Supplier Risk Matrix
A risk matrix makes supplier risk easier to understand and communicate.
A simple 5×5 model can classify suppliers based on likelihood and impact.
| Risk Score | Risk Level | Typical Action |
|---|---|---|
| 1–4 | Low | Standard monitoring |
| 5–9 | Medium | Increased monitoring and periodic review |
| 10–15 | High | Mitigation plan and management review |
| 16–25 | Critical | Immediate review and contingency planning |
These thresholds are only an example. Organizations should define thresholds appropriate to their own risk framework.
Low Risk
The supplier has limited business impact and few significant risk indicators.
Typical action:
- Standard monitoring
- Periodic review
Medium Risk
The supplier has some important risk factors that require attention.
Typical action:
- Increased monitoring
- Additional documentation
- Periodic reassessment
High Risk
The supplier has significant operational, financial, compliance, quality, or other risks.
Typical action:
- Risk mitigation plan
- Management review
- More frequent monitoring
- Alternative supplier evaluation
Critical Risk
The supplier creates a significant potential impact on the organization.
Typical action:
- Immediate risk review
- Executive involvement
- Business continuity planning
- Alternative supplier strategy where practical
Step 6: Mitigate Supplier Risks
Identifying a risk is only the beginning.
The next step is to decide what action should be taken.
Possible risk mitigation strategies include:
- Request additional documentation
- Improve contractual protections
- Increase supplier monitoring
- Establish backup suppliers
- Increase safety stock
- Define corrective action plans
- Conduct supplier audits
- Increase quality inspections
- Require updated compliance documents
- Limit system or data access
- Develop business continuity plans
Every significant risk should ideally have:
- A defined owner
- A mitigation action
- A target date
- A review date
- A current status
The appropriate action depends on the type and severity of the risk.
Supplier Compliance as Part of Risk Management
Supplier compliance should be an important component of supplier risk assessment.
A supplier may initially pass an assessment but become higher risk later because required documents expire.
For example:
A supplier has:
- Valid insurance
- Valid labor license
- Valid registration
- Required statutory documents
At the time of onboarding, the supplier may be considered compliant.
Six months later, an insurance certificate expires.
The supplier’s compliance risk has now changed.
This demonstrates why supplier risk assessment should not be treated as a one-time activity.
Compliance status should be monitored throughout the supplier relationship.
Step 7: Monitor Suppliers Continuously
The assessment process does not end after the initial risk score.
Supplier risk changes over time.
Procurement teams should periodically review:
- Supplier performance
- Delivery performance
- Quality issues
- Compliance status
- Document expiry
- Contract changes
- Business changes
- Risk scores
- Corrective actions
- Financial or operational indicators where relevant
High-risk suppliers may require more frequent reviews than low-risk suppliers.
A risk assessment process should therefore include a defined review schedule.
For example:
| Supplier Risk | Example Review Approach |
|---|---|
| Low | Annual or periodic review |
| Medium | More frequent periodic review |
| High | Regular monitoring and reassessment |
| Critical | Continuous or event-driven review |
The exact frequency should be determined by the organization’s risk framework.
Supplier Risk Assessment During Vendor Onboarding
Risk assessment should ideally begin before a supplier becomes fully active.
A practical onboarding flow can be:
Supplier Identification
↓
Supplier Information Collection
↓
Document Collection
↓
Supplier Risk Assessment
↓
Compliance Review
↓
Approval
↓
Supplier Activation
↓
Ongoing Monitoring
This approach helps organizations identify significant risks before they become embedded in the supplier relationship.
It also connects supplier onboarding with ongoing supplier risk management rather than treating onboarding as a separate activity.
Supplier Risk Assessment Template
A practical supplier risk assessment record can include:
| Field | Example |
|---|---|
| Supplier Name | ABC Engineering Pvt Ltd |
| Supplier Category | Engineering |
| Supplier Criticality | High |
| Financial Risk | Medium |
| Operational Risk | High |
| Quality Risk | Medium |
| Delivery Risk | High |
| Compliance Risk | Low |
| Cybersecurity Risk | Low |
| Likelihood | 4 |
| Impact | 5 |
| Risk Score | 20 |
| Overall Risk | Critical |
| Mitigation Action | Identify alternate supplier |
| Risk Owner | Procurement Manager |
| Next Review Date | Defined by policy |
This structure can be adapted to the organization’s industry and supplier risk framework.
Supplier Risk Assessment Checklist
Procurement teams can use the following checklist as a starting point:
- Supplier identity verified
- Supplier category identified
- Supplier criticality assessed
- Financial risk reviewed
- Operational risk reviewed
- Quality risk reviewed
- Delivery risk reviewed
- Compliance requirements identified
- Required supplier documents collected
- Document validity checked
- Information security risk considered where applicable
- Alternative supplier availability considered
- Risk score calculated
- Supplier risk level assigned
- Risk mitigation actions identified
- Risk owner assigned
- Required approvals completed
- Next review date defined
This checklist should be adapted to the organization’s industry, supplier type, and risk framework.
Common Supplier Risk Assessment Mistakes
1. Assessing Suppliers Only During Onboarding
Supplier risk changes.
A supplier that was low risk two years ago may not remain low risk today.
Risk assessments should therefore be reviewed periodically and when significant events occur.
2. Treating Every Supplier the Same
A critical production supplier should not necessarily receive the same level of assessment as a low-value office supplies vendor.
Risk-based prioritization makes the process more efficient.
3. Focusing Only on Financial Risk
Financial health is important, but supplier risk also includes:
- Operational risk
- Quality risk
- Compliance risk
- Delivery risk
- Cybersecurity risk
- Reputational risk
- Business continuity risk
A supplier can be financially healthy and still create significant operational or compliance risk.
4. Ignoring Compliance Document Expiry
A supplier may remain operational while its required certificates and licenses become invalid.
Expiry monitoring should therefore be part of ongoing supplier management.
5. Keeping Risk Information in Isolated Spreadsheets
When supplier information, risk scores, documents, and corrective actions are maintained in separate spreadsheets, teams may struggle to understand the complete supplier picture.
Centralized supplier information can improve visibility and make ongoing monitoring easier.
6. Not Assigning Ownership
Every significant identified risk should have an owner and, where appropriate, a target action or review date.
Without ownership, risk assessments can become reports rather than actionable processes.
7. Using the Same Risk Score for Every Supplier
A generic scoring model can be useful, but the importance of each risk factor may differ by supplier category.
For example, cybersecurity may be critical for an IT service provider while delivery capacity may be more important for a raw-material supplier.
Risk criteria should therefore reflect the supplier relationship.
How Technology Can Improve Supplier Risk Management
Manual supplier risk assessment can become difficult when organizations manage hundreds or thousands of suppliers.
Technology can help centralize:
- Supplier information
- Risk assessments
- Compliance documents
- Expiry dates
- Supplier status
- Risk scores
- Approvals
- Corrective actions
- Reports
- Audit history
Automated reminders can also help teams act before important compliance documents expire.
Technology can also make it easier to:
- Standardize assessments
- Track review dates
- Maintain supplier history
- Assign risk owners
- Monitor compliance status
- Generate reports
The objective is not simply to automate data entry.
It is to give procurement and compliance teams better visibility into supplier risk and the actions required to manage it.
How VendorCompliancePro Helps With Supplier Compliance Risk
VendorCompliancePro focuses on the supplier compliance component of the broader supplier risk management process.
It provides capabilities for:
- Centralized vendor information
- Vendor document collection
- Vendor self-service
- Document validation
- Expiry tracking
- Automated renewal reminders
- Approval workflows
- Role-based access
- Compliance dashboards
- Audit history
These capabilities can help procurement and compliance teams maintain better visibility into supplier compliance status.
For organizations where supplier compliance is an important part of overall supplier risk, keeping required documents current can help reduce avoidable compliance risks.
VendorCompliancePro can complement an organization’s existing ERP, procurement, or supplier management systems rather than replacing them.
Frequently Asked Questions
What is supplier risk assessment?
Supplier risk assessment is the process of identifying, evaluating, scoring, prioritizing, and managing risks associated with suppliers.
It helps organizations understand which suppliers require greater attention and what actions may be needed.
What are the main types of supplier risk?
Common categories include:
- Financial risk
- Operational risk
- Quality risk
- Delivery risk
- Compliance risk
- Cybersecurity risk
- Reputational risk
- Business continuity risk
The categories used should reflect the organization’s supplier relationships and risk framework.
What is a supplier risk assessment process?
A supplier risk assessment process typically includes:
- Identifying suppliers
- Identifying relevant risk factors
- Assessing likelihood and impact
- Scoring and prioritizing suppliers
- Defining mitigation actions
- Monitoring and reviewing supplier risk
How is supplier risk calculated?
One simple approach is:
Risk Score = Likelihood × Impact
For example, a likelihood score of 4 and an impact score of 5 produces a risk score of 20.
Organizations should define their own scoring thresholds and methodology.
How often should suppliers be assessed?
There is no single frequency that fits every organization.
Review frequency should depend on:
- Supplier criticality
- Risk level
- Business requirements
- Supplier performance
- Compliance status
- Changes in the supplier relationship
High-risk suppliers generally require more frequent review than low-risk suppliers.
What is a supplier risk matrix?
A supplier risk matrix is a framework that compares the likelihood of a risk occurring with its potential impact.
It can help organizations classify suppliers as low, medium, high, or critical risk.
Should supplier compliance be part of risk assessment?
Yes.
Required licenses, registrations, insurance certificates, and other compliance documents can affect supplier risk and should be considered according to the organization’s requirements.
How can organizations prioritize high-risk suppliers?
Organizations can use supplier criticality, risk scores, business impact, likelihood, supplier performance, compliance status, and other relevant risk factors to identify suppliers that require greater attention.
Can supplier risk assessment be automated?
Technology can automate parts of the process, including data collection, assessments, reminders, risk dashboards, document monitoring, approvals, and reporting.
The exact level of automation depends on the organization’s requirements and systems.
Conclusion
Supplier risk assessment is not simply a procurement checklist.
It is an ongoing process for understanding which suppliers could create significant business risk and deciding how those risks should be managed.
A practical supplier risk assessment process includes:
Identify Suppliers → Identify Risks → Assess Risks → Score and Prioritize → Mitigate Risks → Monitor and Review
The most effective supplier risk programs also connect risk assessment with:
- Supplier onboarding
- Supplier master data
- Supplier compliance
- Supplier performance
- Corrective actions
- Ongoing monitoring
When procurement teams have reliable supplier information, clear risk criteria, current compliance documents, defined ownership, and regular reviews, they can make better decisions and respond to supplier risks earlier.
The goal is not to eliminate every supplier risk.
The goal is to understand the risks, prioritize them, and take action before they become costly business problems.
Related Articles
- Supplier Master Data Management: Best Practices
- Vendor Onboarding Process: Complete Checklist
- What Is Vendor Compliance?
- Vendor Compliance Checklist India
- Vendor Document Management Best Practices
- Vendor Audit Readiness Checklist
- Why Vendor Onboarding Still Takes Weeks in 2026
- How AI Can Reduce Vendor Onboarding Time
- Vendor Compliance Software India